-
 Goa plans relationship-readiness course amid concern over divorces
-
Mutual fund returns show shifting leaders across market-cap categories
-
 BHEL wins Adani Power projects valued at up to ₹28,000 crore
-
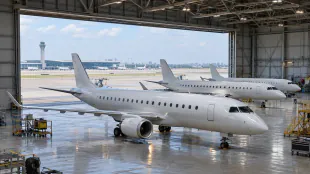
IndiGo holds talks with Embraer over potential order for 100 aircraft
-
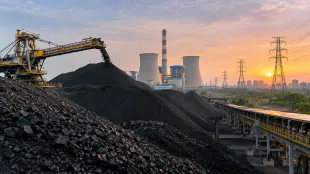 India seeks threefold increase in coal stocks to prevent summer power shortages
-
Indian companies report mixed second-quarter results on November 4
-
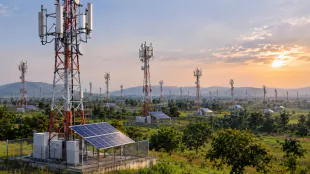 Indus Towers expands solar-powered network to 50,000 telecom sites
-
KKR secures Indian regulator approval for Gentari Renewables investment
-
 Equitas Small Finance Bank rebounds after naming interim chief executive
-
Bharti Airtel revenue expected to grow at double-digit pace in second quarter
-
 Titan quarterly profit seen rising as jewellery business drives growth
-
Indian crude-sensitive shares gain after 13% oil-price decline
-
 Kuwait finance minister holds economic cooperation talks at COMCEC
-
Stocks and dollar fall as Democratic election gains reshape markets
-
 Kuwait marks key events and anniversaries from national history
-
Qatar Tourism joins Pacific Asia Travel Association at London travel market
-
 Qatar media bodies discuss support for humanitarian initiatives
PRIVACY POLICY
PRIVACY POLICY FOR "COIN PRESS"
Version: 31 October 2026.
Data controller
SCANDIC TRUST GROUP LLC
"COIN PRESS"
IQ Business Centre
Bolsunovska Street 13–15
01014 Kyiv / Ukraine
Email: [email protected]
Legal form: limited liability company incorporated under Ukrainian law, LLC.
Ukrainian registration entry: 1010351020000018952.
SCANDIC TRUST GROUP LLC is responsible for processing personal data where it determines the purposes and means of that processing. The company is referred to in this Privacy Policy as “we”, “us” or “our”. "COIN PRESS" is the publication’s title and does not constitute a separate legal entity. The address above is our operational and correspondence address. Privacy enquiries, complaints and requests to exercise your rights may be sent to the email or postal address above.
Registered office and registered address
SCANDIC TRUST GROUP LLC
Oksamytova Street 1-b, Office 30
Sofiivska Borshchahivka
Kyiv Region - 08147 / Ukraine
Technical support and operation
SCANDIC ASSETS FZCO
Dubai Silicon Oasis DDP
Building A1/A2
Dubai - 342001 / United Arab Emirates
Telephone: +971 54 221 5217.
SCANDIC ASSETS FZCO provides technical services supporting the operation of the website. Where it processes personal data on our behalf and under our instructions, the requirements governing processors under Article 28 of the UK General Data Protection Regulation apply. Its permitted access is limited to the processing necessary for its appointment. Whether a company acts as a controller, joint controller or processor depends on its actual responsibilities for the processing concerned; technical involvement or membership of the same corporate group does not, by itself, determine that status.
United Kingdom representative under Article 27 of the UK GDPR
SCANDIC TRUST GROUP LLC
Oksamytova Street 1-b, Office 30
Sofiivska Borshchahivka
Kyiv Region - 08147 / Ukraine
Commercial cooperation
LEGIER Beteiligungs mbH
Kurfürstendamm 14
10719 Berlin
Federal Republic of Germany
Commercial register: HRB 57837
Register court: Amtsgericht Charlottenburg, Berlin
VAT identification number: DE413445833
Telephone: +49 30 99211 3469
Fax: +49 30 99211 3225
Email: [email protected]
Where LEGIER Beteiligungs mbH is involved in an advertising enquiry or commercial arrangement, personal data may be disclosed to it only for a specified lawful purpose and to the extent necessary for its role. Commercial cooperation does not give that company unrestricted access to reader, subscriber or editorial information. Where it determines its own purposes and means of processing, its responsibilities as a separate controller and the relevant privacy information must be identified in connection with the particular service.
United Kingdom representative under Article 27 of the UK GDPR
SCANDIC TRUST GROUP LLC
Oksamytova Street 1-b, Office 30
Sofiivska Borshchahivka
Kyiv Region - 08147 / Ukraine
Introduction and scope
This Privacy Policy explains how personal data are processed in connection with the websites, applications and related services of "COIN PRESS", the purposes and legal grounds for that processing, retention periods and your rights. Provisions concerning accounts, subscriptions, orders, newsletters, reservations or other supplementary functions apply where those functions are offered and used. References to particular external technologies apply where they are incorporated into the relevant service. Processing within the territorial scope of the UK General Data Protection Regulation, referred to below as the “UK GDPR”, is governed by that Regulation and the Data Protection Act 2018, as amended, including the applicable amendments made by the Data (Use and Access) Act 2025. The UK GDPR can apply to an organisation established outside the United Kingdom where the processing concerns offering goods or services to people in the United Kingdom or monitoring their behaviour there. Cookies, comparable technologies and electronic marketing are also subject to the applicable Privacy and Electronic Communications (EC Directive) Regulations 2003, referred to below as “PECR”. This Privacy Policy provides information; it does not constitute consent, and your statutory rights do not depend on accepting it.
A) General information about personal data processing
Personal data are information relating to an identified or identifiable individual. Depending on your interaction with our services, they may include names, contact details, correspondence, account information, transaction records, IP addresses, online identifiers and information about the use of content or functions. Replacing a name with an identifier does not make information anonymous where the individual can still be identified using additional information. We limit processing to data relevant and necessary for the stated purpose, maintain appropriate accuracy and apply data protection by design and by default.
Purposes and lawful bases
The lawful basis depends on the particular purpose and circumstances of the processing.
- Contract and pre-contractual steps: Article 6(1)(b) of the UK GDPR applies where processing is necessary to provide an agreed service or take steps at your request before entering into a contract. Including a processing activity in contractual terms does not, by itself, make that activity necessary.
- Legal obligations: Article 6(1)(c), read with Article 6(3), applies where processing is necessary to comply with an applicable obligation recognised by UK law, including qualifying record-keeping or disclosure requirements.
- Legitimate interests: Article 6(1)(f) may support necessary and proportionate processing for service security, preventing misuse, handling ordinary correspondence, administering business relationships or establishing, exercising or defending legal claims, provided your interests and fundamental rights do not override those interests.
- Consent: Article 6(1)(a) applies where we request your freely given, specific, informed and unambiguous agreement to a defined activity, including relevant optional marketing, personalisation or analytics.
The basis used for one purpose does not automatically authorise another purpose. Consent withdrawal or a valid objection cannot be circumvented by retrospectively assigning a different lawful basis to continue the same processing.
Additional United Kingdom requirements
The Data Protection Act 2018 supplements the UK GDPR, including provisions concerning sensitive information, exemptions, children’s consent, regulatory supervision and remedies. The Data (Use and Access) Act 2025 has amended the framework for individual rights, complaints, automated decision-making, international transfers and certain electronic communications activities. PECR imposes separate requirements for accessing information on devices and sending electronic marketing. A legitimate interest under the UK GDPR does not replace consent where PECR requires it. The recognised legitimate interests introduced by Article 6(1)(ea) concern specified statutory circumstances; they do not provide a general exemption for advertising, profiling or commercial tracking.
Editorial and journalistic processing
Personal data may be processed when researching, preparing, publishing and maintaining journalistic material. Sources may include interviews, correspondence, reader submissions, news agencies, public records, published documents and other sources available to the editorial team. Relevant information can include an individual’s identity, professional activities, statements and matters connected with the subject of reporting. Paragraph 26 of Part 5 of Schedule 2 to the Data Protection Act 2018 provides a conditional exemption for journalism and other specified forms of expression. It applies to listed provisions only where processing is undertaken with a view to publication, we reasonably believe publication would be in the public interest, and we reasonably believe compliance with the particular provision would be incompatible with the journalistic purpose. The special importance of freedom of expression and information must be taken into account. This is not a general exemption for the publisher or all information it holds. Advertising, account administration, subscriptions and ordinary website analytics do not automatically qualify. Public availability, public prominence or an allegation of wrongdoing does not remove an individual’s privacy rights.
External platforms and services
Where our content is made available through external platforms, those platforms may process information for their own purposes. Relevant services may include social networks, video and audio platforms, application stores, connected television services and voice assistants. Their involvement depends on the function you use. Following an ordinary external link and loading an embedded player or image can have different consequences: an embedded component may communicate with its provider before you interact with it. Signing into an external account does not constitute general consent to data being transmitted from "COIN PRESS" to that provider. Each party remains responsible for the processing within its control, including applicable information and consent requirements.
Technical information and voice-assisted services
Technical information may include the requested page or file, date and time, response status, transferred data volume, IP address, browser and operating system information, and a referring page where supplied by the browser. If you access content through a voice assistant or connected device, the platform provider may also process spoken requests, transcripts, device identifiers and account information. The information received by "COIN PRESS" depends on the integration; using a voice assistant does not mean that we receive or retain all recordings made by that device. Information required for operating the requested function must be distinguished from optional analytics or advertising.
Supplementary services and sensitive information
Where a supplementary service requires additional information, such as a reservation, competition entry or event registration, the relevant collection notice explains its purpose, mandatory fields, recipients and retention. We do not require a date of birth, identity document or other additional information merely because a user contacts us. Processing special category data, including health information, political opinions or biometric data used for unique identification, requires an applicable Article 9 condition as well as an Article 6 basis, unless a relevant statutory exemption applies. Criminal allegation, conviction and offence data are subject to Article 10 and the applicable Data Protection Act 2018 conditions. Providing sensitive information voluntarily does not authorise unrestricted further use.
Information obtained from other sources
Where we obtain personal data from another person, an organisation or a publicly accessible source, the applicable information requirements under Article 14 of the UK GDPR remain relevant. Unless a statutory exception applies, we provide the required information within a reasonable period, no later than one month, and earlier where necessary because we first communicate with you or disclose the information. The notice identifies the relevant categories and source of the data, including whether the source was publicly accessible. Journalistic exemptions are subject to the conditions described above.
B) Contacting us
When you contact us, we process the contact details, message content and attachments needed to understand and answer your enquiry. Article 6(1)(b) applies to necessary contractual or pre-contractual correspondence, Article 6(1)(f) to ordinary enquiries and the legitimate interest in responding to them, and Article 6(1)(c) where a relevant legal obligation applies. Sending an enquiry does not enrol you in marketing communications. Correspondence is retained while the matter remains active and, where still necessary, for no longer than 12 months after it is closed. Longer retention is limited to applicable legal obligations or the establishment, exercise or defence of specific legal claims. Please provide only information relevant to your enquiry.
C) Reservations, orders and user accounts
Where these functions are offered, we process the identity, contact, account, order and payment-related information needed to provide and administer the requested service. This may include login credentials, subscription status, delivery preferences and transaction references. Processing necessary for the contract is based on Article 6(1)(b); security and abuse prevention may rely on Article 6(1)(f), subject to the required balancing of interests. Fields necessary for a particular transaction are identified when information is collected, together with the consequences of not providing it. Payment providers may process payment information under their own responsibilities or on our behalf, depending on the arrangement; the relevant provider and role must be identified for the transaction. We do not automatically receive every detail supplied directly to a payment provider. Account and contractual information is retained while necessary for the active relationship and, after it ends, only as set out in section H.
D) Accounting and statutory retention
Invoices, payment records and other accounting documents are retained for the period required by the law applicable to the relevant company and transaction. Where United Kingdom VAT record-keeping requirements apply, records must generally be kept for at least six years, subject to applicable exceptions and special regimes. This requirement does not automatically apply to every record held by an overseas company. Article 6(1)(c) is used only where the relevant obligation satisfies Article 6(3) of the UK GDPR; a foreign statutory obligation does not, by itself, establish that UK lawful basis. Where another lawful basis is required, it must be assessed separately. Statutory retention concerns the records necessary for the obligation and does not justify retaining unrelated browsing, advertising or correspondence data for the same period.
E) Technical provision and operational security
We process necessary technical information to deliver pages and requested functions, maintain availability, diagnose faults, detect attacks and prevent unauthorised access or misuse. The usual basis is Article 6(1)(f), reflecting our legitimate interest in a secure and reliable service; Article 6(1)(b) applies where processing is necessary to perform a particular contract. These grounds do not override PECR requirements. Access to identifiable technical records is restricted according to operational need. Our retention ceiling for ordinary technical records is 12 months from collection, with earlier deletion where the information is no longer necessary. Records relating to a specific incident may be retained separately for as long as required to address that incident or related legal claims.
Cloudflare and cdnjs
Where technical resources are delivered through Cloudflare or the cdnjs content delivery service, the browser communicates with the relevant infrastructure to retrieve those resources. The request may disclose an IP address, the resource requested, request timing and browser or connection information. Processing necessary for reliable delivery or security must have an appropriate lawful basis and comply with the applicable processor and transfer requirements. The use of a content delivery network does not automatically authorise unrelated analytics, profiling or advertising. A browser cache lifetime for a downloaded file is distinct from the retention period for personal data in server or security records.
Google Fonts
Where fonts are loaded directly from Google’s servers, the request can disclose an IP address and technical request information to Google. Where font files are served locally, loading those files does not itself require a direct browser connection to Google. The processing basis must reflect the actual implementation and necessity of the disclosure. A design preference alone does not demonstrate that every associated transfer is necessary. Any storage of, or access to, information on your device must also satisfy the applicable PECR rules. Our own retention periods do not determine how long an external provider retains information for its separate processing.
F) Cookies, device access and tracking technologies
Cookies and similar technologies can store information on your device or retrieve information already stored there. Relevant technologies include browser storage, tracking pixels and certain forms of device recognition. The rules depend on how a technology operates, rather than the name assigned to it. Describing a tool as “cookieless”, “statistical” or “privacy-friendly” does not, by itself, establish that consent is unnecessary. PECR can apply whether or not the information accessed is personal data; where personal data are processed, the UK GDPR applies as well.
Consent and statutory exceptions
Regulation 6 and Schedule A1 to PECR govern storage and access technologies. Prior informed consent is required unless a statutory exception applies. Exceptions include operations necessary to transmit communications and operations strictly necessary to provide a service requested by the user. The amended legislation also permits certain narrowly defined statistical and appearance or functionality purposes without consent, provided all the relevant conditions are satisfied. These include clear information and a simple, free means of objecting where required. The statistical exception concerns improving the service through statistics and does not authorise advertising profiles, unrestricted sharing or tracking across services. The appearance exception does not authorise selecting advertising or editorial content from a behavioural profile. Where an exception depends on the absence of an objection, the relevant storage or access must stop when you object.
Genuine choice and separate purposes
Where consent is required, the relevant function is activated only after a valid affirmative choice. Preselected boxes, silence, continued browsing or general acceptance of terms do not constitute consent. Choices must distinguish purposes sufficiently for an informed decision, and refusing optional processing must be readily accessible. Withdrawal must be as easy as giving consent. Permission to store information on a device does not automatically establish a lawful basis for every subsequent use of personal data. Equally, refusing advertising consent does not authorise the same advertising activity to continue under a different label.
Our preference and consent records
- Cookie choices: we retain the record of your last active choice for no longer than 12 months. Where a cookie named “laravel_cookie_consent” is used for this function, the same limit applies. Its purpose is to respect your choice, rather than identify you for advertising. Another visit does not, by itself, renew consent.
- Language preferences: where a session cookie named “language” records your chosen language, it serves that session preference. Browser session restoration may affect when a session cookie disappears. Any persistent version is limited to the necessary period and no longer than 12 months.
- Changes to processing: materially different purposes or providers require updated information and renewed consent where necessary. A withdrawn choice ceases to authorise processing immediately, regardless of the original expiry date.
These are our retention limits for the relevant preference records, not a statement that UK law assigns a universal 12-month validity period to all cookie consent.
Cloudflare Web Analytics
Where Cloudflare Web Analytics is used, it may measure page views, referral information, loading performance and browser or device characteristics. Cloudflare describes this product as operating without analytics cookies or local storage and without tracking individual users over time through IP addresses or browser fingerprints. Technical communication with the provider nevertheless occurs. Consent-based analytics are activated only after the relevant choice. If a statutory exception is used instead, every condition of that exception must be satisfied, including any required objection mechanism. Cloudflare’s published product information states that unsampled measurement data are retained for seven days before sampling and aggregation, and that historical Web Analytics information is accessible for the preceding six months. These product-specific periods do not establish the retention period for every Cloudflare security or operational log.
Purposes requiring an appropriate individual choice
Where the corresponding functions are offered, purposes may include:
- Using limited information to select advertising.
- Creating profiles for personalised advertising.
- Using profiles to select personalised advertising.
- Creating profiles to personalise content.
- Using profiles to select personalised content.
- Measuring advertising performance.
- Measuring content use and performance.
- Analysing audiences through statistics or information from different sources.
- Developing and improving services.
- Using limited information to select content.
This list identifies possible purposes and does not mean that every activity takes place. Each actual activity requires its own lawful assessment and sufficient information about the providers, data, recipients, retention and relevant transfers. Industry frameworks, including advertising consent frameworks, do not replace statutory requirements or provide an independent lawful basis.
Changing your settings and withdrawing consent
You may withdraw consent through the relevant consent controls where provided or by contacting [email protected]. Where an “Essential only” option is offered, it selects functions necessary for the requested service. You may also use browser settings to block or delete cookies, although deletion alone does not necessarily communicate withdrawal to every recipient. Withdrawal does not affect processing lawfully undertaken before it was withdrawn. Further processing relying on that consent must stop, and data must be deleted unless a separate lawful reason justifies limited continued retention, such as keeping necessary evidence of the choice and its withdrawal.
G) Recipients and international transfers
Personal data are disclosed only for an identified lawful purpose and to the extent necessary. Depending on the service, recipients may include technical suppliers, payment or fulfilment providers, professional advisers subject to confidentiality obligations, and competent authorities or courts where disclosure is lawfully required or otherwise justified. Processors must act within their instructions and applicable contractual obligations. Where organisations jointly determine purposes and means, Article 26 of the UK GDPR applies, including the requirement to make the essence of their allocation of responsibilities available to affected individuals. Common ownership does not provide unrestricted permission to share personal data.
- SCANDIC ASSETS FZCO, United Arab Emirates: technical services and access necessary to perform its appointment.
- Cloudflare, Inc., United States: relevant content delivery, security or Web Analytics functions where those services are used.
- Google and the entity responsible for the particular Google or YouTube service: external resources or embedded content where activated. Depending on the service, relevant entities may include Google Ireland Limited and Google LLC.
- Other suppliers involved in a requested transaction or communication: only where necessary for that service and subject to the applicable information, confidentiality and data protection requirements.
Ukraine and the United Arab Emirates
SCANDIC TRUST GROUP LLC is established in Ukraine, and SCANDIC ASSETS FZCO is established in the United Arab Emirates. Neither country is covered by general UK adequacy regulations at the date of this Privacy Policy. Where processing involves a restricted transfer to a separate organisation outside the United Kingdom, the UK GDPR’s international transfer requirements must be satisfied. Remote access from another country can constitute a transfer even where the server remains in the United Kingdom. A person sending information directly to an overseas controller and a controller subsequently disclosing it to a separate overseas recipient are different situations and require the appropriate legal assessment.
Transfer mechanisms and safeguards
A restricted transfer must be covered by applicable UK adequacy regulations, appropriate safeguards or a valid statutory exception. Appropriate safeguards may include the UK International Data Transfer Agreement or the UK Addendum to the European Commission’s standard contractual clauses, where applicable and binding on the parties. European Commission clauses alone do not automatically satisfy the requirements for a UK restricted transfer. Where safeguards require a data protection test, the assessment must consider whether the protection after transfer would be materially lower than the relevant UK standard, taking account of the circumstances and any supplementary protections. Article 49 exceptions are confined to their statutory conditions and are not a general substitute for safeguards for routine overseas processing. Information about a transfer affecting your data, its applicable mechanism and how to obtain a copy of relevant safeguards may be requested at [email protected].
Transfers to the United States
The UK Extension to the EU–US Data Privacy Framework permits qualifying transfers only to eligible United States organisations with active participation covering the relevant information. Participation in the EU framework alone is insufficient to establish coverage under the UK Extension. The mechanism does not cover every United States recipient or every category of processing, and information transferred for journalistic purposes is outside its coverage. Where the UK Extension does not apply, another valid mechanism is required unless a specific statutory exemption applies. A provider’s general privacy statement does not, by itself, establish that every transfer involving our services is covered.
H) Retention and deletion of personal data
Our ordinary maximum retention period for our own operational records is 12 months, calculated from the relevant event below. We delete information earlier where it is no longer necessary. Longer retention is limited to an ongoing service or contract, a specific legal obligation, the establishment, exercise or defence of legal claims, or a justified journalistic purpose. A maximum period is not permission to retain unnecessary information until that period expires.
- Enquiries and correspondence: while the matter is being handled and, where necessary, for no longer than 12 months after closure, subject to specific legal obligations or claims.
- Accounts and contracts: while necessary for the active account or continuing contract; afterwards, necessary residual information is retained for no longer than 12 months, except for qualifying statutory records or legal claims.
- Technical logs and our own usage records: no longer than 12 months from collection, with earlier deletion where possible. Records of a particular security incident may be retained separately for the period necessary to resolve it or address associated claims.
- Our cookie preference records: no longer than 12 months from the last active choice. This does not extend the validity of withdrawn consent.
- Evidence of consent, withdrawal and objections: ordinarily no longer than 12 months after the consent ends or the matter is closed. A limited record may be kept longer where necessary to respect a continuing marketing objection, comply with a legal obligation or address a specific claim.
- Accounting and tax documents: for the applicable statutory period described in section D, limited to the records covered by that obligation.
- Journalistic materials and archives: for as long as justified by the journalistic purpose and the relevant balance between privacy and freedom of expression and information. This does not authorise indefinite retention of unrelated customer or advertising information.
- Information processed independently by external providers: according to the particular service and the provider’s legal responsibilities. Our 12-month limit neither extends a shorter provider period nor determines the provider’s independent retention.
Deletion requirements also apply to the management of backups. Information awaiting removal through a backup replacement cycle must remain protected from ordinary use, and restoration must not undo previously applicable deletion or restriction requirements.
I) Your rights
Where the UK GDPR applies, you have the following rights subject to their statutory conditions and any applicable exemption:
- Access: under Article 15, to obtain confirmation of processing, access to your personal data, the required supplementary information and a copy of the personal data.
- Rectification: under Article 16, to have inaccurate personal data corrected and incomplete information completed where appropriate.
- Erasure: under Article 17, to have information deleted where a statutory ground applies, subject to exceptions including relevant legal obligations, legal claims and freedom of expression and information.
- Restriction: under Article 18, to limit processing in the circumstances specified by law.
- Portability: under Article 20, to receive qualifying information you have provided in a structured, commonly used, machine-readable format and, where applicable, have it transmitted to another controller, where processing is automated and based on consent or contract.
- Objection: under Article 21, to object to qualifying processing, including the separate unconditional right to object to direct marketing.
- Withdrawal of consent: under Article 7(3), to withdraw consent at any time without affecting the lawfulness of earlier processing based on that consent.
- Automated decision-making safeguards: under Articles 22A to 22D, to receive the applicable information and safeguards in relation to significant decisions based solely on automated processing, as explained in section M.
Where Article 19 applies, rectification, erasure or restriction must be communicated to relevant recipients unless this is impossible or involves disproportionate effort. You may request information about those recipients.
Your right to object
You may object, on grounds relating to your particular situation, to processing based on Article 6(1)(f), including associated profiling. We must then stop that processing unless we demonstrate compelling legitimate grounds overriding your interests, rights and freedoms, or the processing is necessary for legal claims. You may object to processing for direct marketing at any time, without giving reasons. This includes profiling connected with direct marketing. Following that objection, your personal data must no longer be processed for those purposes. A minimal suppression record may be retained to ensure that your objection continues to be respected.
Rights concerning journalistic material
Requests concerning reporting, editorial research, source information or archives are considered under the applicable UK GDPR provisions and the conditional journalism exemption in the Data Protection Act 2018. A request does not automatically require removal of a lawful public-interest article, and an editorial label does not automatically defeat a request. Relevant considerations include the nature and accuracy of the information, its continuing relevance, the effect on the individual, source confidentiality and the public interest in publication. Any restriction must concern a provision covered by the exemption and satisfy its conditions. Ordinary account, subscription and marketing records are not exempt simply because they are held by a newspaper.
Exercising your rights and response periods
Requests may be sent to [email protected] or our correspondence address. You do not need to use legal terminology. Requests are normally free; a reasonable fee or refusal is permitted only where the statutory conditions are met, including for a manifestly unfounded or excessive request. If there are reasonable doubts about identity, we may request only the additional information necessary to resolve them. A full identity document is not automatically required. We respond without undue delay and within the applicable one-month period under Articles 12 and 12A. Where necessary identity information or a lawfully chargeable fee is required, the statutory starting-point rules apply. An extension of up to two further months is permitted where necessary because of complexity or the number of requests, with reasons notified within the initial applicable period. For an access request, the clock may be paused where clarification is reasonably required to identify the information or processing concerned. Searches must be reasonable and proportionate. If we decline a request, we explain the applicable reasons and the available complaint and judicial remedies, subject to lawful restrictions.
Complaints and the supervisory authority
You may complain to us if you consider that the processing of your personal data infringes applicable data protection law. Under section 164A of the Data Protection Act 2018, we acknowledge a qualifying complaint within the statutory 30-day period, take appropriate steps to respond and inform you of the outcome without undue delay. This complaint procedure does not replace the separate deadlines for a request to exercise your rights. You also have the right to complain to the United Kingdom’s supervisory authority, the Information Commission, which continues to use the name ICO. The regulator may ask for the correspondence exchanged with us when considering your complaint.
Information Commission / ICO
Wycliffe House
Water Lane
Wilmslow
Cheshire
SK9 5AF / United Kingdom
Telephone: 0303 123 1113.
J) Security of personal data
We apply technical and organisational measures appropriate to the risks under Article 32 of the UK GDPR, taking account of the nature, scope, context and purposes of processing. Relevant protections concern confidentiality, integrity, availability, access control and recovery from incidents. Security measures must be proportionate to the information and risks involved; no internet-based system can guarantee the complete absence of risk. Where a personal data breach must be reported under Article 33, the supervisory authority is notified without undue delay and, where feasible, within 72 hours of awareness. Where a breach is likely to create a high risk to affected individuals, Article 34 requires communication without undue delay unless a statutory exception applies. Any applicable journalistic exemption must be assessed within its legal limits and does not remove the general obligation to protect personal data appropriately.
K) Privacy disputes and remedies
This Privacy Policy does not restrict your right to complain to the supervisory authority, seek an effective judicial remedy or claim compensation where the statutory conditions are met. Article 82 of the UK GDPR and section 168 of the Data Protection Act 2018 provide for qualifying material and non-material damage, including distress. Financial loss is not invariably required. Entitlement depends on the relevant legal requirements and circumstances; an infringement does not automatically establish every element of a compensation claim. You are not required by this Privacy Policy to undertake consumer arbitration or waive a statutory remedy before exercising your data protection rights.
L) Relevant legislation and case law
The following legislation and decisions are relevant according to the processing concerned and their applicable scope.
United Kingdom legislation
- The UK General Data Protection Regulation: lawful and fair processing, transparency, data minimisation, retention, security, accountability, individual rights and international transfers.
- The Data Protection Act 2018: supplementary processing conditions, exemptions, regulatory powers, complaints and remedies, including Schedule 1, paragraph 26 of Part 5 of Schedule 2, section 164A and section 168.
- The Data (Use and Access) Act 2025: amendments to the data protection and electronic communications framework, including the provisions in force concerning individual requests, automated decision-making, complaints, transfer assessments and storage or access technologies.
- The Privacy and Electronic Communications (EC Directive) Regulations 2003: in particular regulation 6 and Schedule A1 on device storage and access, and regulations 22 and 23 on electronic marketing.
- The Human Rights Act 1998 and Articles 8 and 10 of the European Convention on Human Rights: the protection of private life and the balancing of privacy with freedom of expression and information.
- The Value Added Tax Act 1994 and applicable record-keeping requirements: retention of qualifying tax records where the relevant company or transaction falls within their scope.
Relevant judgments
- Campbell v MGN Limited [2004] UKHL 22, judgment of 6 May 2004: protection of private information and the balancing of privacy against freedom of expression, including the particular sensitivity of information about health and treatment.
- Bloomberg LP v ZXC [2022] UKSC 5, judgment of 16 February 2022: as a legitimate starting point, a person under criminal investigation has a reasonable expectation of privacy concerning that investigation before being charged; the circumstances and competing public interests remain relevant.
- Lloyd v Google LLC [2021] UKSC 50, judgment of 10 November 2021: limits on the representative compensation claim advanced under the Data Protection Act 1998 and the requirement, under the provision considered, to establish material damage or distress rather than rely on a uniform award for the infringement alone. The decision does not abolish the rights to compensation available under the current UK GDPR and Data Protection Act 2018.
M) Additional information about individual services
Newsletters and electronic marketing
Where newsletters are offered, the subscription information identifies their purpose and the relevant use of your contact details. Consent-based subscriptions rely on Article 6(1)(a) of the UK GDPR and the applicable PECR requirements. Unsolicited electronic marketing to individual subscribers requires consent unless a statutory exception applies. The commercial “soft opt-in” is limited to contact details obtained during a sale or negotiations for a sale, marketing of our own similar products or services, and a clear, simple opportunity to refuse at collection and in every subsequent message. It does not authorise marketing to an acquired list or unrestricted promotion by other group companies. Different PECR consent rules apply to corporate subscribers, but applicable UK GDPR duties, sender identification and an effective means of stopping messages remain relevant. An account registration or ordinary enquiry is not, by itself, marketing consent. You may unsubscribe using the facility in the message or by contacting [email protected].
Email measurement and subscription records
Subscribing to a newsletter does not automatically authorise individual tracking of message openings or link use. Such tracking requires appropriate information and a lawful basis, including consent where PECR requires it. Subscription information is retained while the subscription continues. Following withdrawal, necessary residual records are ordinarily retained for no longer than 12 months, subject to the limited exceptions in section H. A proportionate suppression record may be kept longer to prevent renewed marketing against your wishes. Messages strictly necessary to administer a requested service are distinguished from promotional messages by their actual content and purpose.
Embedded content, social networks and affiliate links
External video or audio players, social features, images and other embedded components may disclose an IP address, device information, the page visited and interaction data to their providers. This can occur even if you have no account with the provider. Where you are signed in, the provider may be able to associate activity with that account. Components requiring consent must not be activated before valid consent is obtained. Referring to an external privacy policy does not replace the information or consent obligations for processing under our responsibility. Receiving commission from an affiliate link does not, by itself, provide a lawful basis for tracking you.
YouTube
Where a video is provided through YouTube, both the player and an externally hosted preview image may communicate with Google or YouTube infrastructure. A preview can therefore disclose technical information before the video is played. Activating the player may involve further information about playback and interactions and the use of cookies or similar technologies. The processing depends on the integration, device settings and account status. A description such as “privacy-enhanced mode” does not remove the need to assess the actual processing. Consent-based activation relies on Article 6(1)(a), with separate compliance with regulation 6 and Schedule A1 to PECR where information is stored on or read from your device.
Examples of Google cookie durations
Google identifies the following examples for its services. Their actual use depends on the service, region, account status and configuration.
- YSC: a session cookie used for security-related purposes.
- __Secure-YNID: a cookie used for YouTube functionality and troubleshooting, with a stated duration of six months; it replaces VISITOR_INFO1_LIVE.
- PREF: a cookie recording playback and presentation preferences, with a stated expiry of eight months after the user’s last use.
- SOCS: a cookie recording Google cookie choices, with a stated duration of 13 months.
These examples do not mean that every cookie is set through our services. A cookie’s lifetime is distinct from the retention of account information or server records by the provider. The information given for an actual integration must describe the technologies and purposes applicable to that integration.
Profiling and automated decision-making
Personalisation may involve evaluating identifiers, viewed content or interactions to infer interests or preferences. This may constitute profiling, although not every personalised recommendation or advertisement amounts to a decision having legal or similarly significant effects. Articles 22A to 22D of the UK GDPR govern significant decisions based solely on automated processing, meaning decisions without meaningful human involvement. Where such a decision is made, the applicable safeguards include information about the decision, the opportunity to make representations, human intervention and the ability to contest it. Stricter conditions apply where the decision is based wholly or partly on special category data: the statutory explicit-consent condition or the specified combination of a contractual or legal ground and substantial public interest must be satisfied. Significant solely automated decisions cannot rely wholly or partly on the recognised legitimate interests basis in Article 6(1)(ea). Where a service uses relevant decision-making, the required information about its operation, significance and consequences must be provided before the processing concerned.
Children and young people
Children’s information requires particular protection and explanations appropriate to their understanding. Where an information society service is offered directly to a child and consent is the lawful basis, Article 8 of the UK GDPR and section 9 of the Data Protection Act 2018 set the United Kingdom consent age at 13. For a child under 13, the required consent must be given or authorised by a person with parental responsibility, with reasonable verification efforts appropriate to the circumstances. This is not a general minimum age for reading publicly accessible journalism and does not determine a child’s capacity to enter into a contract. Where the Age Appropriate Design Code applies to an online service likely to be accessed by children, relevant safeguards include consideration of their best interests, suitable privacy defaults, data minimisation and appropriate controls over profiling and location information. Age assurance must itself be necessary and proportionate.
Changes to this Privacy Policy
We may update this Privacy Policy to reflect changes to services, processing practices or legal requirements. Before using personal data for a new purpose, we provide the information required by law and obtain fresh consent where necessary. Publication of an updated policy, silence or continued use of a service does not constitute consent to new processing. Existing consent may be withdrawn at any time. The date below identifies the latest revision of this Privacy Policy.
Contact:
COIN PRESS
Email: [email protected]
© 2026 "COIN PRESS" - All rights reserved, subject to statutory exceptions.
Last updated: 31 October 2026.